

Last week, I was giving a talk in Boston. On the inauspicious date of Friday the 13th, I boarded a flight back to Washington, D.C. I got on the plane, put away my luggage, and settled into my little seat. Ten minutes before we were scheduled to taxi, the flight attendant announced that the entire plane would have to disembark. “Apparently some wires got crossed at the FAA,” he said, “but don’t worry, the delay should only be about an hour.” We all got off the plane. I pulled out my phone. Within minutes, our delay had become the top story on CNN, ABC, and the New York Times homepage. Every flight in the U.S. had been halted, in just the third ground stop of the century. I rented a car and drove home.
The FAA outage was just the beginning. Or, perhaps, the middle of the beginning. The previous week, Microsoft services went down. On Monday, United Airlines experienced its own tech outage. On Tuesday, several banks including JPMorgan and Bank of America said customers couldn’t withdraw funds due to a software bug; then the NSA announced that its communications systems were hit with another outage; then Apple announced its own difficulties; then, the FBI issued a FLASH advisory warning that cybercriminals and state-aligned hackers were using AI to attack businesses and organizations around the world.
Well, shit.
What’s happening to the world? One imagines several possibilities.
We’re under attack: This is a coordinated and systemic AI hack. This is the cyberpocalypse that we’ve been waiting for.
We’re breaking the Internet in our efforts to save it: Perhaps these outages are related, not to AI’s offensive capabilities, but rather to its defensive capabilities. As companies use AI to discover vulnerabilities in their existing software, engineers are rushing to fix the problem, and that rush is causing a bunch of failures.
Maybe it’s all a frequency illusion: Some analysts suggested that the number of outages isn’t statistically abnormal, but the news media is more sensitive to outages than it used to be because of fears about AI destroying the world.
To understand what’s really going on, and what will happen next, I spoke to two experts. Nicole Perlroth is a cybersecurity expert who spent years as a reporter before starting a company that specializes in understanding cyber vulnerabilities. Jennifer Pahlka is an author and former Deputy Chief Technology Officer of the US government, who has written deeply on why government technology sucks and what it would take to improve it. (I’ve adorned our conversation with several graphs from JPMorgan’s 2026 analysis of what it calls “Patchmageddon.”)
As you read the interviews with Perlroth and Pahlka, look out for these three critical points:
Like a soccer team that accidentally scores an own-goal because the defenders and goalie are under pressure from talented strikers, many companies feeling the heat from escalating AI attacks are accidentally crashing their own systems by rushing “patches” to fix urgent cyber vulnerabilities. This week’s mess has been mostly the result of defensive patching, but the next cavalcade of outages might be the result of attackers that get through the defense.
We can’t fix government technology, like our air traffic control system, by throwing more money into a broken system. We have to fix the system itself by bringing more technological expertise into government.
Thanksgiving Week is a very, very good time to clean up your password hygiene, add a password manager, and move to two-factor authentication.
Nicole Perlroth: America’s Digital Deficit Is Coming Due
Derek Thompson: How would you describe what’s transpired in the last week?
Nicole Perlroth: We have a great digital deficit in this country. The digital deficit is that we have been rolling out flawed code, leaving that flawed code in systems, and we haven’t been updating it for years. We’ve also been baking code into every nook and cranny of our economy, critical infrastructure, our homes, our cars, our bodies in some cases. No one ever stopped to think that we were just adding and adding to this digital deficit that would one day come due.
With AI, it is now coming due in a big way. AI models have tremendous capabilities to find vulnerabilities in code and exploit it to break into systems on the other side. So all of these errors that we rolled out in this code and never addressed are now being found by these powerful models and stitched together in such a way as to attack systems.
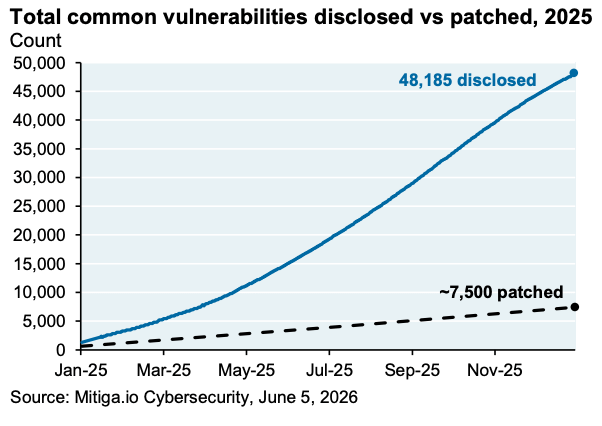
We are finding three times the number of vulnerabilities using AI this year than we were in the same period last year. Attackers are exploiting those vulnerabilities using AI at a much quicker rate than we’ve ever seen. By the time a company learns it has a flaw in its code and rolls out a patch, it turns out that, on average, attackers have already been exploiting that flaw for seven days.
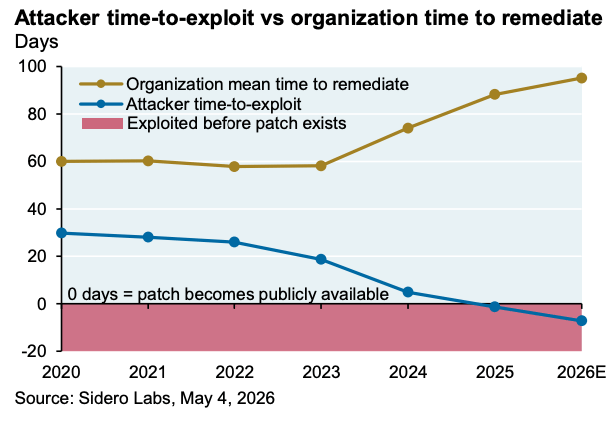
What this means is that while we used to be able to live on this Patch Tuesday cycle, where companies would roll out fixes for vulnerabilities in their code and customers would have time to update their systems, now we’re on the attacker’s schedule. So companies and government agencies are finding it very urgent to install these patches and software updates. It’s really easy to find a vulnerability now and exploit it. It’s still really hard and time consuming to properly install a patch. And when you install a patch, you do it in these bespoke environments. No environment is the same. You can’t just push a big red button and everything’s fixed. Usually something will break on the other end.
What we have seen over this past week of outage after outage is companies and government agencies installing these patches and software updates to fix vulnerabilities that were discovered with AI, and they are breaking things on the other end. So these are not cyberattacks, but the impact is the same.
Thompson: You made two important points that I want to make sure I understand. Advanced AI has offensive capabilities to discover cyber vulnerabilities and attack. But what we’ve seen over the last few days is not hackers breaking into systems. Rather, sophisticated AI tools are finding vulnerabilities, and the patches themselves are coming in so fast that they’re causing their own breakages. Is that right?
Perlroth: Two things are true at the same time. AI is absolutely increasing the number of incidents and the velocity of these incidents. And it’s much harder to triage these incidents because when you’re hit with an agent, it doesn’t follow the same workflow as a human attacker.
What happened with these outages that are almost simultaneous, the FAA, the bank disruptions, United Airlines, the NSA net outage, is that those are companies or organizations that are trying to get ahead of this huge tsunami of AI-powered attacks by installing software updates as quickly as they come. And those software updates have not gone through the proper quality control and testing that they might have in an earlier pre-AI era. And they are breaking things on the other end.
Thompson: Are there actually more outages now than in previous weeks or months, or are we paying closer attention because we’re sensitive to the imminence of a cyber apocalypse? Does anyone keep a baseline for how often critical systems fail?
Perlroth: I saw some people use AI to conduct a timeline analysis of whether we’ve had these outage clusters before. And we absolutely have. It’s not the first time we’ve had simultaneous outages or near-simultaneous outages. So I do think you’re right that a lot of this is baked into the attention that is on AI right now. I don’t know that we’ve had outages in these very public systems, critical infrastructure, that would capture our attention in the same way. For years I have been warning about two critical infrastructure systems in particular that kept me up at night.
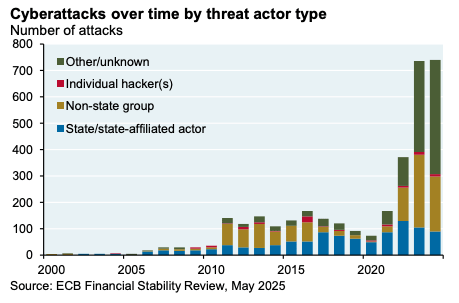
People ask me: What keeps you up at night? And I’ve always highlighted two potential scenarios. One, an attack on our water treatment facilities that would contaminate the water or lead to a water shutoff. And two, an attack on air traffic control.
This Substack is reader-supported. To receive new posts and support my work, consider becoming a free or paid subscriber.
Why Water Systems Are Vulnerable
Thompson: What makes them so vulnerable?
Perlroth: A few years ago, there was a hack, and we still don’t even know whether it was a hack, on a water treatment facility in a town in Florida just outside the city hosting the Super Bowl that year. The way the story was initially relayed to us, an engineer was watching his screen and this ghost mouse moved across his screen, moved over to the chemical controls, and increased the amount of lye in the water and could have potentially poisoned everyone downstream.
When we started digging into this, it was pretty terrifying to get a sense of the state of cybersecurity around our water treatment facilities. There is unfortunately a very big story of the haves and have-nots in cybersecurity. Companies like JPMorgan, Goldman Sachs, the banks, and certain critical infrastructure providers have the budgets to be able to buy every bell and whistle in cybersecurity. But the little guys don’t.
Water treatment facilities are notoriously underfunded, understaffed, and often have to rely on outside contractors who remote in to manage things like the chemical levels in the water. And that naturally creates an opening for hackers. Often the people who set these systems up were not thinking about the fact that one day an Iranian hacker might want to contaminate the water supply in the United States. So often they do it with the poorest cyber hygiene—like using “password” for a password, or being without two-factor authentication.
We actually can’t have a system of haves and have-nots in cybersecurity. We’re an ecosystem. And if the most critical part of that ecosystem breaks, it’s going to break the big guys too. Water is the one that is probably the most susceptible to an attack, even though it’s the most critical.
‘This Is Definitely the Opening Chapter’
Thompson: If we’re going to be patching faster than ever to get ahead of potential cyber attacks, should people expect more outages like this in the near future?
Perlroth: This is definitely the opening chapter. We haven’t seen until really the last couple months nation states and cyber criminals start leveraging autonomous offensive AI attack tools to come for organizations, but they are now.
And we are also seeing attack frameworks like ARTEX dropped in their lap. These are tools that can leverage different models to search for, find, exploit vulnerabilities at machine speed. A couple of these were part of an FBI advisory just this week. And it adds pressure on companies to fix these vulnerabilities and run these software updates as much as possible.
So we are in a very compressed window right now, not just because of the added pressure from these autonomous attack tools, but also because we’re just ahead of Thanksgiving and the holidays. A lot of organizations want to run these updates just before the holidays so they’re protected going into that cycle.
But this is just the early innings of these models. These are, we always say, the least sophisticated of these capabilities we will ever see. And as I wrote in my book, there are as many vulnerabilities out there as there are stars in the sky. It might not be infinite, but we have truly failed to take quality control of software seriously for decades.
Even if magically tomorrow we were able to leverage AI to write secure code, there are a lot of systems out there running legacy code that can’t update their systems even if they want to, that can’t even get a patch if they want to. This really is the digital deficit coming due.
I think once we have enough of these very public critical outages, we will see the political will and summon the budgets to finally rip and replace these old legacy systems. But even that will cause a lot of pain in the process because naturally it will lead to things like misconfigurations and cascading failures.
It needs to happen, because the idea we’re just going to sit around while AI attackers are able to leverage every vulnerability, chain them together for successful attacks on critical systems, it’s a hell we don’t want to walk towards. There will be a lot of pain and flickering and outages in the near term.
Thompson: When I think about warnings about a digital deficit coming due, my mind turns to Y2K. How does the Y2K metaphor serve us and dis-serve us?
Perlroth: Y2K is like the other extreme, right? You don’t want to scare people and then all of a sudden you look around and everything’s fine.
But Y2K was baked around one timing issue. What we’re talking about now is near-infinite vulnerabilities in all kinds of code that AI is finding. It’s able to stitch together vulnerabilities that humans couldn’t before, again, with our puny little brains, and exploit them at machine speed.
With Y2K, we were talking about one vulnerability in essence. Now we’re talking about many different potential vulnerabilities that AI is turning up across many different hardware and software configurations. And because we baked that code into so much more critical infrastructure than we ever had in our Y2K moment, it’s going to impact our livelihoods in a much more real way.
The Era of Autonomous Attacks
Thompson: Yesterday the FBI issued a flash advisory warning that cybercriminals and state-aligned actors are using AI to attack organizations around the world using something called ARTEX. At the same time, Google’s threat intelligence group said, “The era of autonomous attacks has arrived.” What is ARTEX, and what makes it so dangerous?
Perlroth: ARTEX is essentially a tool that makes a lot of different kinds of autonomous attacks as easy to execute as pushing a button. It automates the process of leveraging these models to scan for and exploit vulnerabilities in systems on the other end. So someone who has no technical expertise whatsoever can now leverage this tool to find vulnerable systems and attack them by pressing the easy button.
What that means is that attack capabilities that once were the province of an advanced nation state or cyber criminal group now potentially belong to a much broader pool of people. Third-tier nation states that never really had the capability to execute an attack by chaining different vulnerabilities together can now use ARTEX to do so. And there are a lot of entities like that that wish to do the United States harm.
We’ve seen Iran probing our water treatment facilities. North Korea is much more financially motivated. While we’ve seen them use some zero-days in their attacks, they didn’t specialize in finding and exploiting zero-days. But now these AI models make it much easier for them to do so.
When you think about a ransomware attack, a lot of it was manual. You had to find vulnerable companies to attack. You needed to go through a list of those companies to find out how many are actually worth hacking, how many are likely to pay, how many have cyber insurance policies. Then they had to find the systems of interest or the data to encrypt. Then they had to manage the payment negotiation.
All of that has now been fully automated using these tools. You can use the prompt: Find me systems of interest that are likely to pay a $10 million ransom, find the data of interest to encrypt, and manage the payment negotiation for me for maximum psychological pressure. Done.
Those tools have now fallen into the laps of cyber criminals, nation states, what I call digital arsonists, people who just have some sick fixation with watching the world burn. That dynamic is going to lead to far more incidents. And again, we are running out of bandwidth on the incident response side. When you call 911 now in breach response, the most likely answer you’re going to get is: We have to turn you away. Sorry, we’re busy.
For organizations, that means they have to get ahead of this thing. And that means running software updates as quickly as possible, even if it might break something on the other end. So this is just going to keep happening.
As far as Google’s threat intelligence group’s warning, that is not new news, but it means more coming from Google’s threat intelligence group. We’ve seen these attacks get some automation over the last two years. It’s just that now we’re getting closer and closer to full automation.
Where—and When—Are the Major Cyber Attacks?
Thompson: The outages from the past week were mostly on the defensive side. But you, the FBI, and Google are also saying an era of offensive attacks is coming. If we’re looking for headlines about offensive attacks shutting down American infrastructure systems, we don’t seem to have seen that yet. Where are we in the cyber offense timeline?
Perlroth: I will be very frank here and say that I don’t think the cybersecurity reporting out there is capturing how many attacks are playing out right now. If you talk to any CISO, a chief information security officer at a major company, they will tell you: We are under constant attack from autonomous attackers or AI-enabled attackers. It is constant. It’s hitting us thousands of times a day.
So that is absolutely happening. My understanding, having talked to some of them, is that companies critical in back-end payment infrastructure and critical in staffing and hiring contractors were the target of a significant extortion attack from an AI-enabled attack just in the past two weeks.
I was hosting a bunch of chief information security officers at a conference just a week and a half ago. And there were many attendees who could not show up because they were all being targeted simultaneously with this spate of extortion attacks.
There is a lot that is not getting reported right now. People have not paid enough attention to cybersecurity. Covering cybersecurity at the New York Times was a very big uphill battle. Trying to get editors to care about cybersecurity was a huge uphill battle for me. Eventually I decided I’m going to stop writing about this problem and go join the guys who are trying to solve it.
There are attacks happening all the time, and the signal that you need to look at is that we are out of bandwidth on incident response. CrowdStrike just completely reorganized itself. People who are at the top of the company, who haven’t triaged an incident or led an incident response in years, are getting dragged in to lead incident response right now. Law firms that are paid on retainer and specialize in helping their clients manage incident response can’t fulfill their obligations right now.
So that is the blinking red light. And I think we need to do a lot better job trying to figure out where the breaches are happening and how it might break things in the supply chain.
When the Cyber Pearl Harbor Arrives
Thompson: AI is already very unpopular, before any obvious hit to jobs or offensive cybersecurity. Some major AI-assisted attack on a critical piece of infrastructure seems likely to happen. What happens to the AI discussion after a critical attack is confirmed?
Perlroth: It’s really interesting because for years cybersecurity experts have told me, we’re going to have a cyber 9/11, we’re going to have a cyber Pearl Harbor. But it never happened. And I would always ask them, so when is this event going to happen? Almost comically, they would always say, 18 to 24 months, Nicole. Eighteen to 24 months. It’s just short enough to add urgency, but just long enough that I might not hold them to it if it didn’t come true.
I think actually we are in that critical 18-month period where we are going to see systems that we have taken for granted stop working. As far as how that’s going to shift the AI conversation, I welcome that moment in some ways as someone who’s been warning about this for years. It was very frustrating when we had our Mythos moment, when Dario and Anthropic came out and said, we’re going to withhold this model from public consumption because we see it has very powerful cyber capabilities. It was very frustrating to see the reaction from the administration, even from people in the cybersecurity industry who said this is all marketing. ARTEX is proof of what Anthropic was trying to warn everyone about with Mythos, which is that these models have very real offensive cyber capabilities, and they are going to be thrown in everyone’s lap and come back to bite us.
My hope is that the conversation will be a nuanced one. There were two things that collided over the decade that I covered cybersecurity for the New York Times. One was “move fast and break things.” Just get your app, get your whistle to market as quickly as possible. You can worry about the security problems later. Mark Zuckerberg. And the other was Marc Andreessen: “Software eats world.” Let’s get software into every nook and cranny of our physical infrastructure. It will add to our efficiencies. It will make our lives better. It might save costs. It’ll allow us to remotely monitor an issue on an oil rig hundreds of miles offshore. No one stopped to say, wait a minute, should we be putting code into everything? Should we be digitally connecting everything? What happens when this becomes attack surface?
And now we’re about to see what happens when all of that code presents as an attack surface that can be leveraged and exploited against us at machine speed. I think we’re in for a very big wake-up call. And my hope is that we will have much more nuanced conversations around: Should we be digitizing everything? Are there some systems that are so precious to us that we should keep them analog, that we should air gap them, that we should make it mission critical that no one can access this system from the internet?
How to Prepare for Cyber Chaos
Thompson: Within this window of pain, what should people actually do to protect themselves?
Perlroth: The advice I always give people, and I also give it to companies, is identify the thing that is most precious to you and harden it as much as possible. So if you are a company and you’re Coca-Cola, and your most precious thing is your IP or the formula for Coke or your mergers and acquisition strategy or your factory real estate strategy, don’t leave that open for anyone at the company to find. Add several layers of hardening and multifactor authentication around it. Continually ask yourself: Does [the internet] actually need access to this?
Jennifer Pahlka: Why the Government Sucks at Technology
Derek Thompson: The FAA ground halt and the NSA communication outage have drawn a lot of attention and a lot of conspiracy theories. What do you think is the story to focus on?
Jennifer Pahlka: The real story of what’s different with the FAA versus the [private-sector] outages is that government doesn’t own these systems. We outsource all this stuff. And that makes it really hard for government to learn and get better. If you look in the history of the FAA, there’s actually quite a few that have gone down over the past couple decades and then the past couple of years. And to me, that’s a sign of an organization that’s outsourced not just its network but has also outsourced the expertise and the knowledge and the ability to learn and adapt, and that doesn’t work.
Thompson: Let’s slow down on the FAA ground stop. This is just the third time this century we’ve had an FAA ground stop, but it’s the second time in the last few years. Is it useful to see this as a pattern? And if so, what is it a pattern of?
Pahlka: I think we’re seeing a pattern of politicians saying, “When something goes wrong, give us more money.” And we have been giving them more money and it’s not making things go better. In government, we treat problems like, “Let’s keep all the planes in the air.” Or, “Let’s make a website that everyone can use to sign up for their health insurance.” Or, “Let’s help kids apply for financial aid,” as problems of contracting. And so the people who get applied to the problem are people who understand how to hire a vendor to do a job. They are not necessarily the people who [understand] the technology.
More Money Won’t Fix the Problem—It Will Make the Problem Worse
Thompson: We’re hearing Transportation Secretary Sean Duffy demanding more money at news conferences every day. He says Congress needs to pony up another $50 billion to upgrade the air traffic control system. As specifically as possible, can you explain why giving Sean Duffy and the Department of Transportation another $50 billion does not solve the problem?
Pahlka: Well, first of all, you can tell from the escalation of the requests from $10 billion to $30 billion to $50 billion that these are not engineering-driven numbers. This is someone really pulling it out of his butt, so to speak, and just saying more money. It comes from a belief that more money is better, when it is the upgrading that is creating the outages, so there’s a logical problem there.
But you want me to be specific about what happens inside of bureaucracy. The bigger the number that you are given to contract out, the more contracting and procurement and compliance people get involved, the more complex the contracts become, the more you have to specify all of these different things, and the more you lock us in to what’s available right now and ways of working now. And a lot of these contracts take a really long time. So by the time that the contractor is working on them, they’re working off requirements that were often written 4, 10, 15 years ago. The technology world has moved on and that’s actually not the way to solve the problem anymore. But I think the biggest reason that these things go south when you give them more money is this balance of power between the kinds of expertise that you want to apply to the problem.
These aren’t bad people. They’re good people who are trying very hard to do the right thing, but you’re basically saying, “Let’s put more contracting and compliance expertise on this problem and we will drown out the voices of the people with the technical understanding to know what should have happened that day in Arkansas that didn’t happen that caused the outage.”
Thompson: Here’s Michael Boyd, an aviation consultant writing in the New York Times [“$50 Billion Won’t Fix Air Traffic Control. It Needs to Be Scrapped.”]
Just this month, the FAA proudly announced that air traffic control will be free of floppy discs by 2028. Memo to the agency, it’s not the floppies that are the problem, it’s the system they are plugged into. Over the past 40 years, I estimate tens of billions have already been spent on the same organizational and functional approach that has given us the rickety system that collapsed last week….
The agency has a track record similar to that of a used car lot. There’s been a parade of grand air traffic control upgrade schemes over the decades with flashy names like FANS and STARS…. The latest FAA bromide is something called BNATCS or Brand New Air Traffic Control System … All the while, the F.A.A. has been issuing glowing reports of how it was installing new equipment, establishing new approaches, hiring more controllers and changing air transportation forever.
We saw the fruits of these changes when according to officials, a simple router upgrade somewhere in Arkansas cascaded into a national ground stop.
Is the problem that government technology is bad, or is the problem that government technology expertise exists outside of government?
Pahlka: Michael is right. Let me add to his analysis here with another example. I worked on unemployment insurance backlogs during the pandemic. Everybody blamed the COBOL system. That’s the equivalent of his upset about everyone blaming the floppies. It’s not the COBOL, right? In the case of unemployment insurance, it’s the 7,119 pages of regulations that govern it that make it a very, very hard system to get right. It’s always going to be incredibly complex and therefore pretty fragile.
But the thing you should know about unemployment insurance is that about half of the states had “modernized” before COVID hit. On average, those states did no better than the states that hadn’t. Everyone thinks that what we need to do is modernize government technology. The way that I put it, which I think is resonant with Michael’s statement, is we need to modernize how we modernize.
We keep trying to throw more money into a system that does not deliver results. Our current way of building and buying technology is not a machine for delivering results. It’s a machine for spending a lot of money and creating a lot of mess that often sets us back, because then people have less faith in it.
I’ve spent 15 years doing this. My focus for 10 years was on the technology side of it, and I came to the conclusion that you can’t solve government technology at the level of the technology. It’s the operating model that government runs on that dictates why we spend our money this way. It’s a very heavy waterfall system where you do a lot of upfront planning, and then the goal is to stay incredibly faithful to the plan and execute it exactly as it was laid out.
That’s a system that worked really well when we built this new administrative state coming out of the Great Depression and to fight World War II. It is not a system that gets us results in this day and age. And so the way to get the right technology in government is to go upstream and fix what’s going on in government more broadly and shift it to an operating system that tests and learns its way to success.
A Better Way Forward for Public Technology
Thompson: If the people in charge of unemployment insurance technology, or air traffic control systems, were first and foremost technical domain experts in government with support from some procurement staff, what would be different?
Pahlka: Well, you can see this. We have natural experiments. When you bring people in-house on things like the FAFSA, it gets better. And by the way, it also gets cheaper. And the reason it gets better is because you’ve got people who you can just walk over to in the office and say, “Let’s try this thing. We can learn that it works or it doesn’t work. If it doesn’t work, we roll it back. If it does work, we scale it out.” And that’s how things get better. Everything you use today got better because people did that. When you contract everything out, and I’m not saying we can’t contract stuff out, but when you contract stuff out through this very heavy waterfall process where you’ve defined everything upfront, you will not learn that something didn’t work until potentially 5 to 10 years after it was specced out. That just means that stuff is going to not work.
Thompson: It seems like a part of the problem here, if you go all the way upstream, is that government doesn’t have the right kind of people in the first place. How do we change that? How do we create a government where the people in charge of processes like air traffic control or unemployment insurance or student loan programs have technical expertise and are empowered to build technology that the government understands how to run and modernize?
Pahlka: I do want to start by saying we do have a lot of great tech talent in government. Very often it’s sort of a power struggle between them and others. I talk about the six-person tech team surrounded by the 60-person compliance team, and that is changing.
Your question was how do we change it, and I think it’s going to be hard. It is actually the key focus of my work now at an organization called Recoding America, where we think that government needs to change its operating model fundamentally. And the first piece of that is we need the right people in the right roles. People think that’s about things like the hiring processes, which are not great, I agree, but it is fundamentally the question that you asked: who do we hire and what kind of skills and expertise do we put on a problem that government needs to solve?
I would point to two things. One, we are going to have to completely rewrite our civil service statutes. At the federal level, this is all rolled up into something called Title V. The last real revision of it was 1947, I believe. People will talk about the Civil Service Act of ‘79, but it really just nibbled around the edges. We created the civil service system that runs our federal government in very much an industrial era. It is not fit for the purpose that we need it to serve, and we need a powerful bipartisan political coalition pushing for fundamental reforms.
This has not been on anyone’s dance card. It is getting to be on the dance card. The organizations that I work with are pushing it onto the dance card, and there are two senators that are interested in this. There’s members of the House interested in it. And at the state level, North Carolina has already rewritten its civil service statute. It passed unanimously. A red legislature, signed into law by a blue governor.
So there’s real momentum here, and that I think is how you get out of the rut that we’re in and into a world of, “Hey, we live in a very fast-paced AI world. What is the job we need to hire for that will consistently get us the outcomes that the American public is asking for?” And then the second piece of it is this belief that came around in the ‘80s of government can’t do anything, so let’s outsource everything. It has not worked out well. I think we have a lot to do to just bust open the myth that the private sector does it all better.